Cybersecurity for regulated businesses
Offset Risk. Enable Growth.
Offset Security helps businesses strengthen cyber resilience, manage risk, and achieve information security, privacy and regulatory compliance. From continuous monitoring to strategic security guidance, we bring expertise and accountability under one roof.
Works with the tools you already run
Nine practices. One senior team.
We identify, manage and reduce cyber risk across your technology, your people and your governance, and we stay accountable for the result.
Find and fix exposure
Know what you run, find what is exposed, and close it before an attacker does.
Detect and respond
Watch every device and account around the clock, and act fast when something gets through.
Govern and prepare
Prove control to auditors and boards, and get ahead of what changes next, from regulation to quantum.
A security department, not another platform license.
We are the practitioner-led team between your operations and the threats targeting them. We watch your environment around the clock, stop attacks before they spread, and keep you audit-ready.
Beyond standalone tools
Growing environments quickly outgrow standalone tools. Real security needs a dedicated team, not another license.
Platforms aren’t protection
Many vendors sell a platform, configure a dashboard and call it protection. As your infrastructure scales, your risk outpaces your software.
Judgment when it matters
When a critical incident hits in the middle of the night, you don’t need another alert. You need someone with the judgment to contain it.
Your security department
We are not a reseller. We work as your internal security architecture and response team, accountable for the outcome.
Post-quantum readiness
The encryption protecting you today won’t survive quantum computing.
NIST has published the replacements for RSA and elliptic-curve cryptography. We find every place you use cryptography, rank what is most exposed, and migrate you to the new standards without breaking production.
- 2024The standards are finalNIST publishes FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA).
- 2025Hybrid encryption goes mainstreamMajor browsers and cloud providers switch on hybrid post-quantum key exchange by default.
- 2026 TodayMigration is the job nowRegulators and customers expect a cryptographic inventory and a plan. Data stolen today can be decrypted later.
- 2030RSA and ECC deprecatedNIST’s transition plan retires quantum-vulnerable algorithms for most uses.
- 2035Quantum-vulnerable crypto disallowedLarge migrations take years, so the work has to be under way now.
Built for regulated sectors.
All sectors- HealthcareDefending patient care when seconds count.HIPAA, HITECH, NIST CSF
- Finance & InsuranceResilience for high-value transactions.GLBA, SEC disclosure, PCI DSS 4.0
- ManufacturingSecuring the production line from IT to OT.CMMC 2.0, NIST 800-171, IEC 62443
- GovernmentProtecting citizen trust and public infrastructure.NIST 800-53, StateRAMP, CISA
- EducationSecuring open networks in academic ecosystems.FERPA, GLBA, SOPIPA
- AutomotiveSecuring the connected automotive supply chain.TISAX, ISO/SAE 21434, UN R155
Free security tools, on your own server.
Six ready-to-run apps built by our team. No cloud account, no license server, and nothing leaves your network.
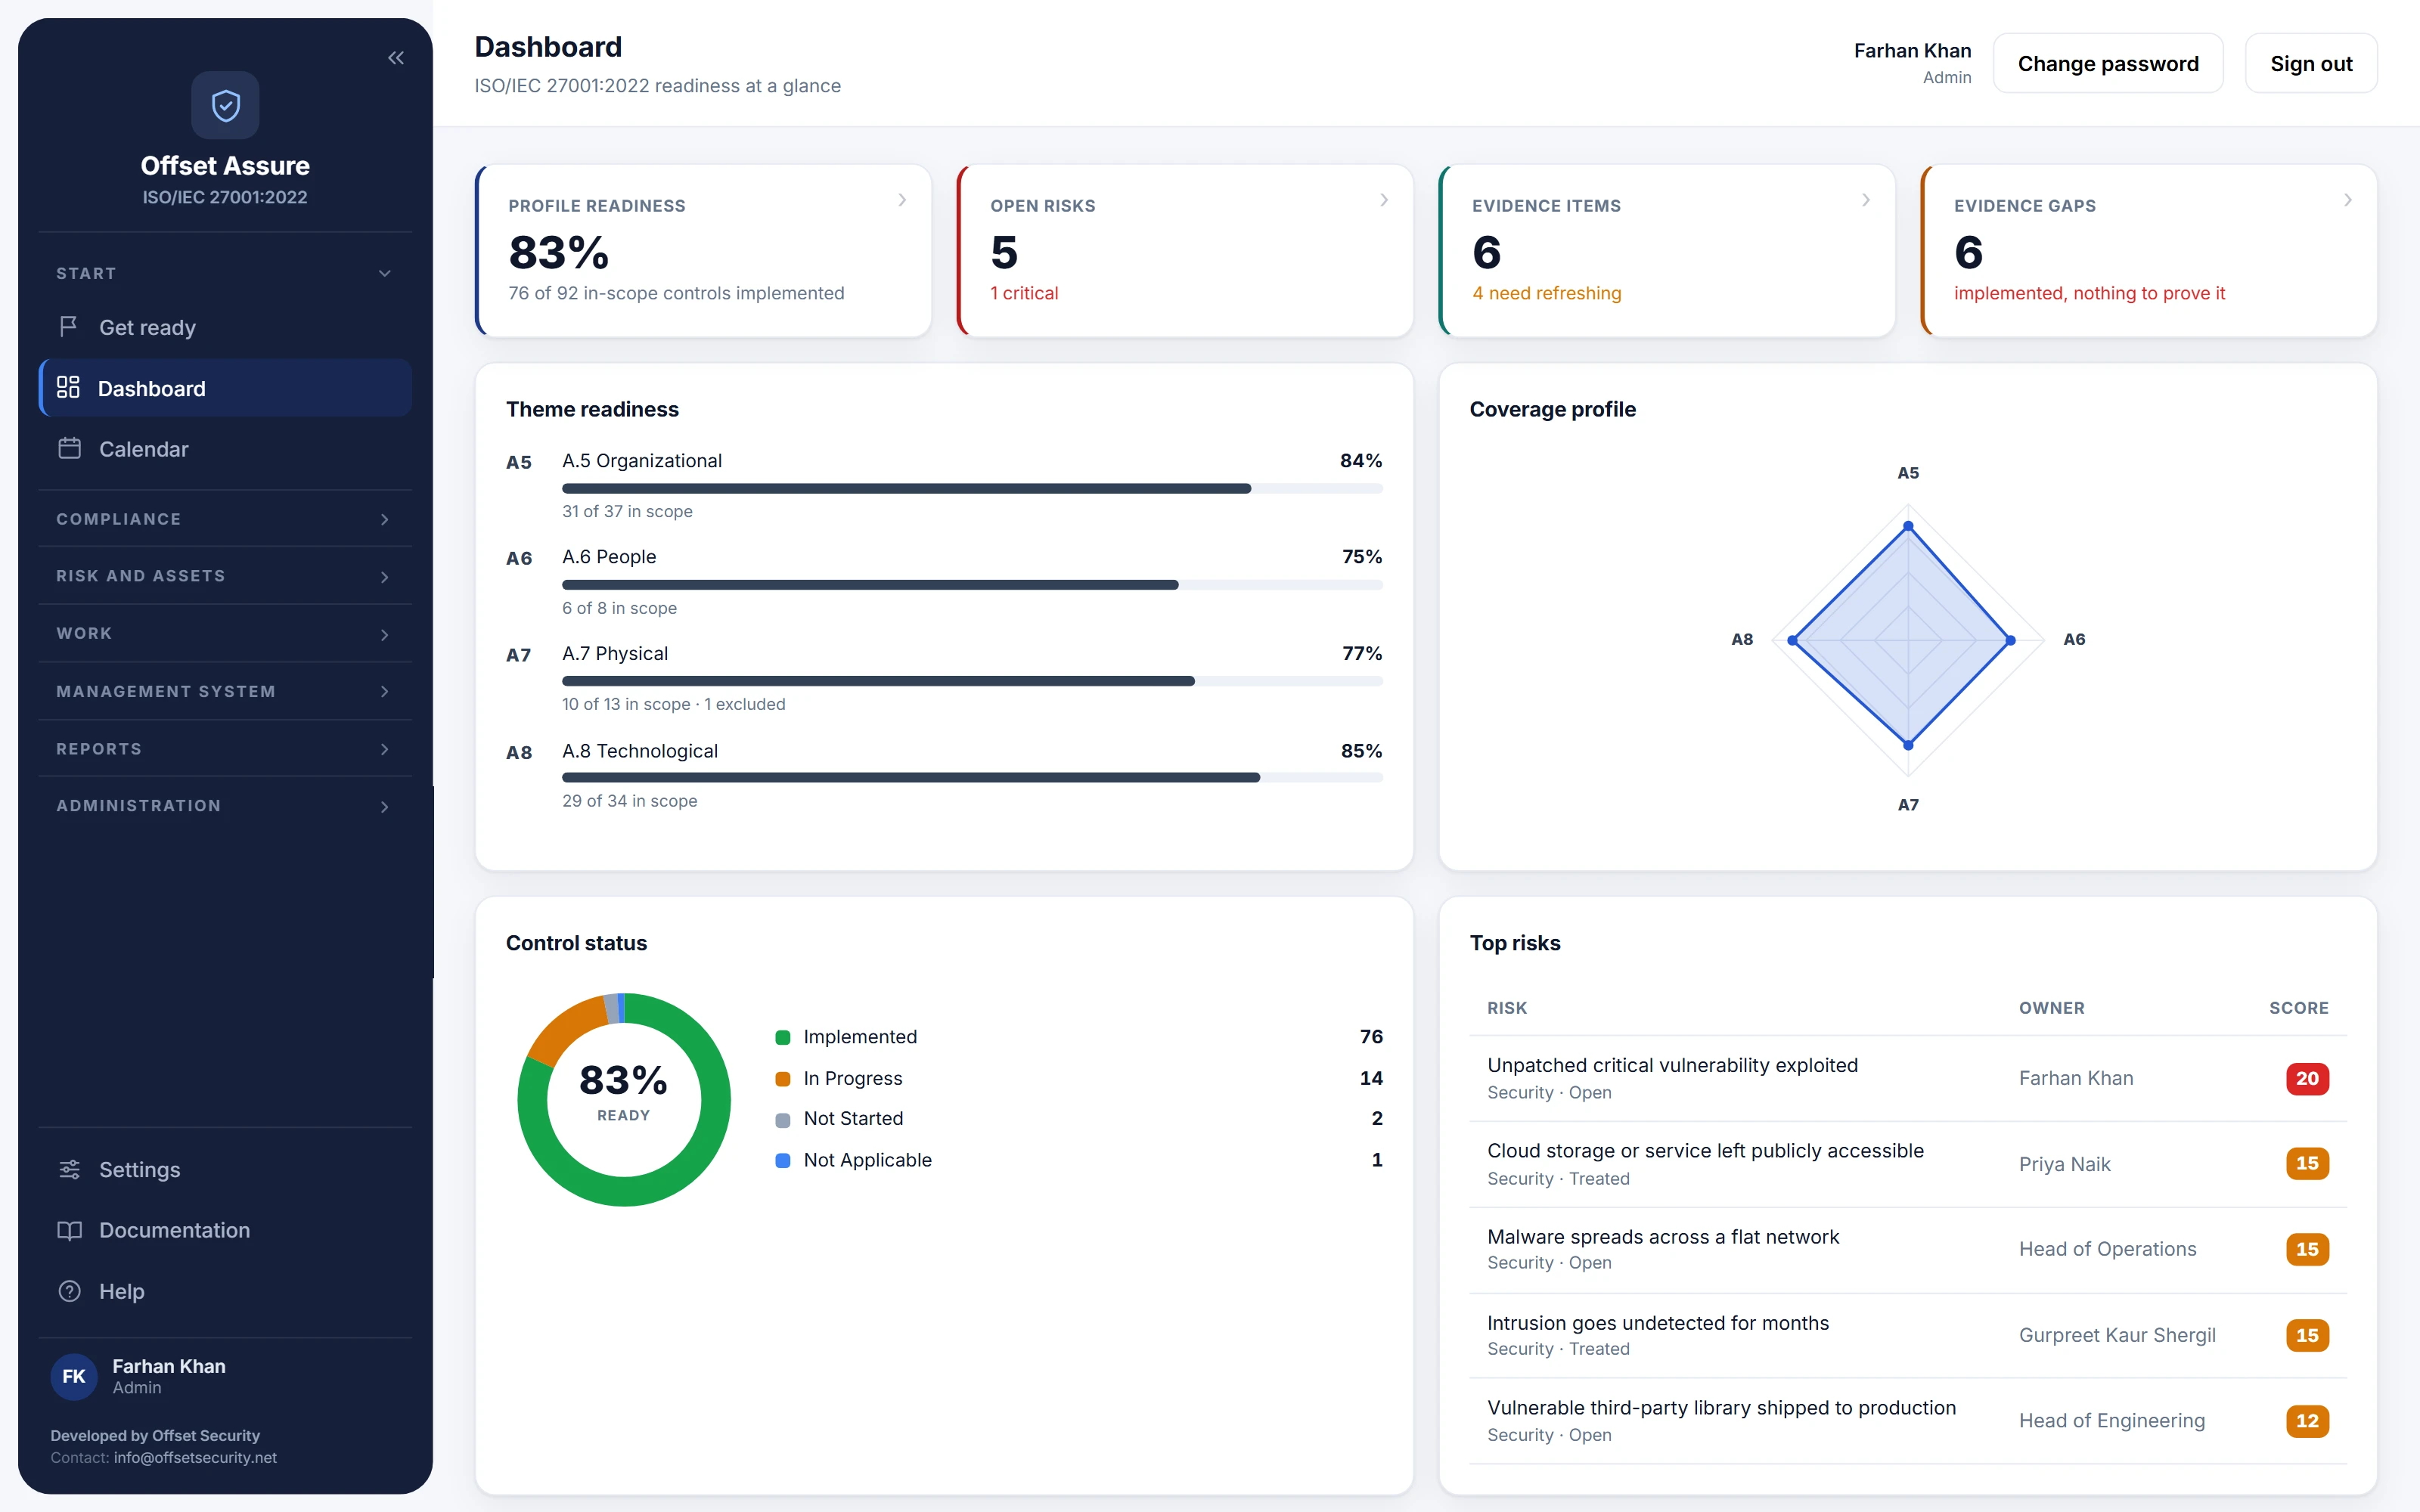
- ISO 27001Offset Assure
- SAMA CSFOffset Irtiqa
- HIPAAOffset Abide
- NIST SP 800-53 · NIST CSF 2.0Offset Anchor & Align
- Security awareness trainingOffset Aware
Ready to offset your risk?
Get three specific recommendations for your infrastructure from a senior security engineer. No sales deck, no obligation.
What happens next
- 01Expert reviewA senior practitioner reads your note and looks at your environment.
- 02Discovery callNo pitch and no generic demo: a technical conversation with specific recommendations.
- 03Scoped proposalIf you want to go further, we scope the work around what you actually need.